What Is the EU Cyber Resilience Act (CRA) and What Does It Mean for the Payment Industry?
A new European regulation is about to become a market-access condition for anyone selling products with digital elements or remotely processing data into the EU: the Cyber Resilience Act (CRA), formally Regulation (EU) 2024/2847. If your organisation builds a payment application, operates an acquiring gateway, issues certificates or distributes cryptographic keys to terminals, or manufactures the terminals themselves, this regulation now sits on your compliance roadmap alongside the standards you already know well.
What is the EU Cyber Resilience Act?
The CRA sets mandatory cybersecurity requirements for products with digital elements made available on the EU market. Compliance results in CE marking, which makes the CRA a condition for selling in the EU.
The regulation came to life to address two main issues observed on the EU market:
- Inconsistent security management in connected products. Connected products available on the EU market are regularly subject to cybersecurity issues. Vulnerabilities or security alerts on severe incidents are identified but answers provided to address these security topics, in terms of communication as well as in terms of security fixes and updates, are globally inconsistent leading to potential hole in the security shield
- Limited information for product users. The information shared with product users (business users or end users and consumers) may be scarce, especially in terms of visibility on the product lifecycle and support timeline. This limited knowledge leads to a crucial lack of trust and reliability on the products’ overall security.
The CRA has been designed to establish a harmonised cybersecurity framework for products with digital elements, enhancing product security and giving the users and consumers of these products greater assurance that appropriate cybersecurity measures are being implemented throughout the product lifecycle. The Regulation consolidates previously fragmented national requirements across EU Member States into a single, consistent regulatory framework, introducing common product classifications, essential cybersecurity requirements, and conformity assessment processes. It also establishes a unified approach to vulnerability reporting and security alert mechanisms across the European Union, promoting consistent incident handling and strengthening the overall cybersecurity resilience of the EU digital ecosystem.
The outcome of the CRA program is to deliver their individual CE marking to each in scope product.
Who does the CRA apply to?
The CRA applies to manufacturers, importers and distributors of products with digital elements made available on the EU market, regardless of where the company is based.
- Manufacturers: those who design, develop and manufacture products made available on the EU market.
- Importers: those who place non-EU products on the EU market.
- Distributors: those who make products available on the EU market without being manufacturers or importers.
Which products are in scope of the CRA?
The CRA applies to products with digital elements (PDE): hardware or software products that require a logical or physical data connection to a device or network to fulfil their main function purpose. The PDE definition also includes the product's remote data processing solution. Therefore a PDE can take several forms or include different components typologies: a hardware device, a standalone application, a firmware, a service, an embedded application and its backend process.
Although applying the regulation results in the product CE-marking, it is therefore not hardware-specific as one could anticipate. Software applications and solutions are in scope as long as they are part of a product with digital elements made available on the EU market.
Some products are excluded, mainly because their cybersecurity is already covered by dedicated European regulations:
- National security and defence (Art. 2(2))
- Medical devices (MDR Regulation (EU) 2017/745 and IVDR Regulation (EU) 2017/746)
- Civil aviation (Regulation (EU) 2018/1139)
- Marine equipment (Directive 2014/90/EU)
- Motor vehicles (Regulation (EU) 2019/2144)
- Non-commercial open-source software.
Does CRA apply to the payment industry?
The objectives of the CRA regulation align closely with the payment industry's cybersecurity concerns. Organisations operating within the payment ecosystem should view CRA as a product-wide cybersecurity regulation rather than one that applies solely to hardware devices. It certainly affects hardware products like POS terminals and HSMs, and requires the CE marking requirements to be updated to align with those of the CRA regulation, but its scope also extends beyond that. Software solutions which are embedded in payment devices or are remotely made available to the market are also definitely to be considered in the context of this regulation.
The following illustration identifies several generic use cases deployed in the payment industry. Each of them is to be carefully considered to determine how it is impacted by CRA, which ones of its components fall into CRA scope, how critical they are, hence which compliance program applies.
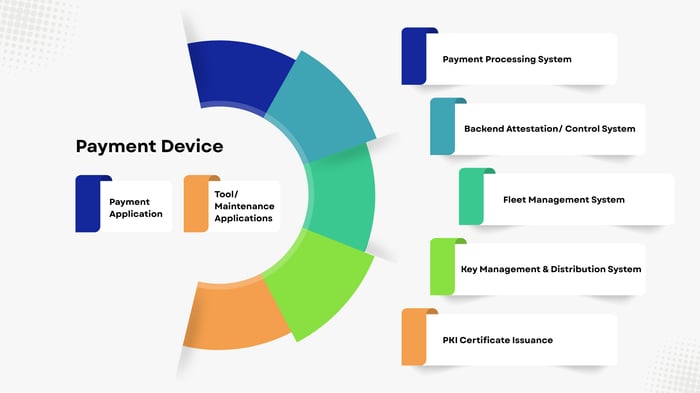
To understand how CRA applies to each product and solution, a fundamental question will have to be answered: what is the core function of the product? In other words, will the product still work and provide the expected service if we remove such or such part of the product?
CRA requirements impact on products cybersecurity management
The CRA is a global EU regulatory program with its own content and timeline. Firstly, the CRA relies on 4 pillars in terms of cybersecurity:
- Essential cybersecurity requirements which apply to design, development and production of the product;
- Vulnerability Handling Obligations which must be carried out on each product for its defined support period
- Obligations for economic operators: manufacturers, importers, distributors, authorised representatives
- Market surveillance and enforcement authority applied at each Member State national level
Depending on the type of product and the level of data sensitivity it operates you won’t expect the same compliance path. For this purpose the CRA defines 3 typologies of products which lead to different levels of compliance enforcement and conformity programs. The level of risk increases alongside the category criticality:
- Default products
- Important products, (Class I or Class II)
- Critical products
A product's classification depends heavily on its core functionality. As a consequence, each product requires a specific analysis to determine its category. The EU regulation 2024/2847 has been complemented by the Commission Implementing Regulation (EU) 2025/2392 to further identify the important and critical products.
CRA timeline: key dates and deadlines
The CRA takes effect in stages: reporting obligations start on 11 September 2026, and the full requirements, including CE marking, apply from 11 December 2027.
|
Date |
What activates |
Who it affects |
|
11 June 2026 |
Member States must have designated the national notifying authorities responsible for assessing, designating and monitoring conformity assessment bodies (i.e., the bodies that will become "notified bodies") |
Notified bodies preparing to offer CRA assessments; manufacturers planning ahead for their assessments |
|
11 September 2026 |
Reporting obligations become active: manufacturers must notify actively exploited vulnerabilities and severe incidents via ENISA's Single Reporting Platform |
All manufacturers of in-scope products, including those already on the market |
|
11 December 2027 |
The full essential cybersecurity requirements, conformity assessment, CE marking, and market surveillance/enforcement provisions apply |
All manufacturers, importers, distributors placing in-scope products on the EU market, or updating substantially existing ones. |
In parallel with the implementation of the CRA's essential cybersecurity requirements, several horizontal harmonised standards are currently under development and are expected to be published over the coming months. Demonstrating products compliance with the harmonised standards, when relevant, is an authorized alternative path to demonstrate CE conformity.
Whereas the full set of requirements apply after 11 December 2027 to all new products made available on the market or to already existing ones that undergo a substantial change, the reporting obligations as of 11 September 2026 apply to all products, meaning the already deployed products as well.
Who are the actors involved in the CRA?
The CRA framework relies on three types of actors at European, national and local level:
The program relies on different local, national and European actors, namely:
- ENISA, the European Union Agency for Cybersecurity: the central cybersecurity management authority who make the Single Reporting Platform available to product owners to simplify the reporting process and facilitate the communication of vulnerabilities, security alerts and security updates and fixes to product users;
- National authorities in each Member State: Each Member State national authorities body who are managing the local notification process and monitor the notified body’s assessments. Here we are mainly referring the national CSIRTs — the same computer security incident response teams many payment organisations already have a relationship with through national cybersecurity frameworks;
- Notified bodies: the organisations designated at national level to carry out conformity assessments.
Non compliance to this statutory regulation may lead to very large penalties:
- up to €15 million or 2.5% of worldwide annual turnover, whichever is higher, for breaches of the essential cybersecurity requirements;
- up to €10 million or 2% of worldwide annual turnover, whichever is higher, for breaches of other obligations, such as those placed on importers and distributors;
- up to €2.5 million or 1% of worldwide annual turnover, whichever is higher, for supplying incorrect, incomplete, or misleading information to an authority or notified body.
Beyond fines, market surveillance authorities can order product withdrawal or recall — a materially worse outcome for a payment platform provider than the fine itself, given the operational and reputational cost of pulling a gateway or terminal fleet out of production.
Integrating CRA into Payment Security
The CRA regulation objective is not to add an extra layer to the security compliance millefeuille but to make sure that the overall product and security is enforced with the right level of expectations relative to the cybersecurity risks carried by each product.
As previously mentioned the payment industry encompasses a large number of products and use cases which require individual review to identify the right classification and to apply the right assessment process.
Identifying and classifying the products, reviewing the security design, analysing the risk, and assessing the security conformity is what Foregenix specialises in in the payment industry. Rather than introducing an additional security layer, the CRA complements existing regulatory and industry frameworks by providing a standardised governance model for the cybersecurity of products and digital solutions. Foregenix's approach to supporting organisations with CRA compliance is based on building upon existing cybersecurity governance rather than introducing parallel processes. The objective is to:
- Leverage established security governance frameworks and secure development processes already in place within the organisation.
- Enhance these frameworks to simultaneously support multiple regulatory, certification, and assessment programmes, including the CRA, while avoiding duplicated efforts.
- Provide security, engineering, and compliance teams with a consistent and integrated approach to managing product cybersecurity throughout the entire product lifecycle, from design and development to deployment, vulnerability management, customer communication, and end-of-support.
By adopting this approach, organisations can transform CRA compliance from a standalone regulatory exercise into an integral part of their overall product security governance, creating efficiencies across multiple compliance frameworks while strengthening the cybersecurity and resilience of their products.
Conclusion
The CRA represents far more than a new regulatory requirement; it marks a fundamental shift in how cybersecurity is expected to be embedded into products with digital elements throughout their entire lifecycle. For the payment industry, compliance cannot be treated as a hardware-only exercise or as a simple extension of existing certification processes. Manufacturers, software providers, payment service providers, and other economic operators must now adopt a product-centric approach that integrates cybersecurity by design, continuous vulnerability management, and clear governance from development through end-of-support. Organisations that begin assessing their product portfolios, identifying applicable conformity paths, and aligning their secure development and vulnerability handling processes today will not only be better prepared for the CRA deadlines but will also strengthen customer trust and improve the resilience of the European payments ecosystem as a whole.
Frequently asked questions
-
What is the EU Cyber Resilience Act in simple terms? The Cyber Resilience Act is an EU regulation that requires products with digital elements made available (either in return of payment or free of charge) in the EU to meet cybersecurity requirements throughout their support period. Products that comply obtain CE marking, which becomes a condition for access to the EU market.
-
Who must comply with the CRA? Manufacturers, importers and distributors of products with digital elements made available on the EU market. This includes companies based outside the EU whose products are sold in the EU.
-
When does the CRA take effect? In stages. Reporting obligations for actively exploited vulnerabilities and severe incidents start on 11 September 2026. The full requirements, including conformity assessment and CE marking, apply from 11 December 2027. Reporting obligations also cover in-scope products already on the market.
-
Does the CRA apply to software, or only to hardware? Both. The CRA covers hardware and software products, including standalone software, firmware and remote data processing solutions, as long as they are part of a product made available on the EU market.
-
What happens if a product is not CRA compliant? Enforcement is handled by national market surveillance authorities, and the penalties are substantial. Non-compliance with the essential cybersecurity requirements or with the reporting obligations can lead to administrative fines of up to EUR 15 million or 2.5% of total worldwide annual turnover, whichever is higher. Other infringements carry fines of up to EUR 10 million or 2% of turnover (Article 64 of Regulation (EU) 2024/2847). Fines can be applied in addition to other corrective or restrictive measures.
-
Do existing certifications like PCI DSS or Common Criteria satisfy CRA requirements? Partially. Existing certifications cover some of the controls the CRA requires, but the CRA introduces obligations that none of them fully addresses. A scoping review maps what is already covered and identifies the real gaps.
Subscribe to our Blog
Sylvie Vigier
Sylvie Vigier is an experienced Information security consultant with over 20 years experience in information security field, including 14 in the payment industry. She has led organization in their security transformation, setting up governance, developing strong operational process to reach robust and consistent security framework capable of satisfying international and regional security standards and regulations. She is now focusing on supporting organizations along their journey to understand and comply with the recently defined European regulations with a single objective: improve their security posture to protect their business and that of their customers and partners.
See All Articles